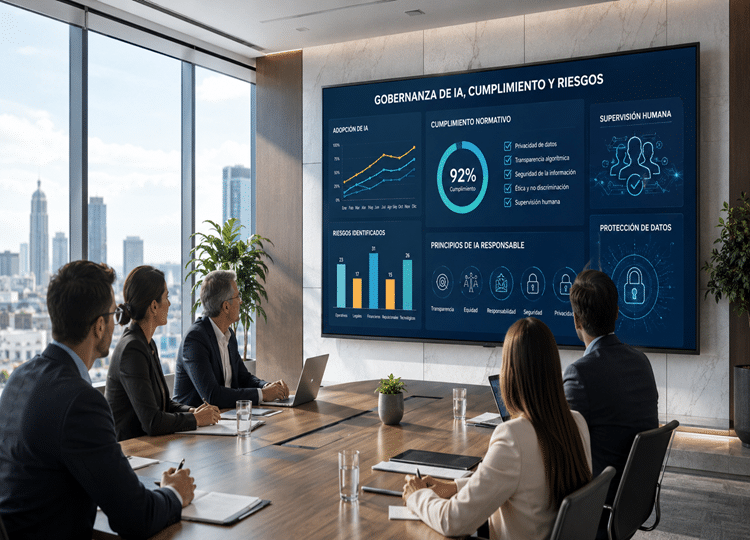
How does the AI Act affect the way businesses use artificial intelligence?
Artificial intelligence (AI) has evolved from being a promising technological innovation into an everyday business tool. In just a few months, assistants such as ChatGPT, Microsoft Copilot and Gemini have become part of the daily operations of many organisations, helping them prepare commercial proposals, summarise meetings, draft contracts, analyse information and automate administrative tasks.
In many organisations, AI has also been adopted by departments such as marketing, human resources, legal and sales long before it reached the boardroom.
When a business integrates artificial intelligence tools into its internal processes, it does more than change the way it operates; it also assumes new legal responsibilities.
This has become particularly significant following the adoption of Regulation (EU) 2024/1689, commonly known as the Artificial Intelligence Act (AI Act), whose implementation timetable makes 2 August 2026 a key date for businesses and organisations across the European Union.
There remains a widespread misconception that the AI Act is aimed exclusively at large technology companies. In reality, an SME that implements chatbot on its website, uses AI tools to draft reports, generates marketing content using artificial intelligence or relies on AI to support certain internal processes may also become subject to specific obligations under the AI Act, even if it has never developed its own AI system.
The question, therefore, is no longer simply whether a business should adopt artificial intelligence. The real question is whether it is prepared to use AI in compliance with the new European regulatory framework.
AI and business: from data protection compliance to AI governance
The entry into force of the General Data Protection Regulation (GDPR) fundamentally changed the way organisations manage information, requiring them to review procedures, amend contracts, implement internal policies and provide staff training.
The AI Act represents a similar shift. Its purpose is not to restrict innovation or prohibit the use of artificial intelligence, but rather to ensure that these technologies are deployed safely, transparently and in a manner that respects fundamental rights.
In other words, the AI Act introduces a new framework for corporate AI governance.
Just as it would now be unthinkable for organisations to process personal data without complying with the GDPR, it will increasingly become unacceptable to use AI tools without internal rules governing how they may be used, who is authorised to use them and under what conditions.
The use of AI does not displace the application of other legal obligations
One of the most common misconceptions is to analyse the AI Act as though it were a self-contained piece of legislation. In reality, the use of artificial intelligence operates alongside the wider legal framework and has implications for legislation with which businesses are already familiar.
For example, where an employee uploads a contract to an AI platform to generate a summary, uses customer information to prepare a commercial proposal or asks an AI tool to draft a report based on internal documentation, the obligations arising under the GDPR, national data protection legislation, intellectual property law, trade secrets legislation and contractual liability remain fully applicable.
Accordingly, organisations must understand which AI applications are actually being used, what information is shared with them, who provides the service, where the data is hosted and whether the provider is entitled to reuse that information for the purpose of training its models.
These issues should form the starting point of any serious AI Act compliance project.
AI literacy: an obligation that many businesses are still unaware of
Although public debate often focuses on high-risk AI systems, for most small and medium-sized enterprises some of the AI Act’s most significant obligations relate directly to their day-to-day business activities.
A good example is Article 4 of the AI Act, which requires organisations to take measures to ensure that individuals using AI systems on their behalf possess a sufficient level of AI literacy.
This provision deserves careful consideration. The Regulation does not simply require businesses to provide a training course. It goes considerably further, requiring those who use AI systems to have an appropriate understanding of how they function, their limitations, the risks associated with their use and the organisation’s internal policies governing their deployment, together with the applicable legal framework.
In practice, this requires organisations to incorporate artificial intelligence into their staff training and awareness programmes, just as they have already done with data protection, cybersecurity and corporate compliance.
Training therefore ceases to be merely advisable and becomes a legal obligation as well as a tangible expression of an organisation’s duty of care.
Transparency in the use of AI: an obligation with greater implications than many businesses realise
Alongside AI literacy, the Regulation introduces another requirement that businesses may overlook if they focus exclusively on high-risk AI systems.
This concerns the transparency obligations laid down in Article 50 of the AI Act.
The principle underlying this provision is straightforward: individuals are entitled to know when they are interacting with an AI system or when particular content has been generated or manipulated through artificial intelligence.
For that reason, compliance with the AI Act should begin with an internal audit designed to identify which AI tools are being used, for what purposes and under what conditions.
On the basis of that assessment, organisations can then implement AI usage policies, train their personnel, review contractual arrangements with technology providers and establish appropriate mechanisms for human oversight.
AI governance is not about prohibiting the use of artificial intelligence; it is about ensuring that it is used in a structured, documented and legally compliant manner.
The real AI risk often lies within the organisation
Businesses often focus on selecting AI platforms that offer the highest standards of security and privacy. However, compliance with the AI Act does not depend solely on the technology provider.
Two organisations may use exactly the same AI tool while presenting entirely different levels of legal and operational risk. The difference lies in how that tool is implemented and governed within the business.
It is increasingly common for individual departments to use AI applications without the knowledge of senior management, for employees to rely on personal accounts for business purposes, or for confidential information to be uploaded to external AI platforms without first assessing their terms of use. Likewise, AI-generated documents are frequently incorporated into day-to-day business activities without adequate human review.
In such circumstances, the issue is no longer purely technological. It is organisational.
For this reason, Article 26 of the AI Act, which establishes certain obligations for deployers of AI systems, places particular emphasis on ensuring that AI systems are used in accordance with the provider’s instructions, that appropriate human oversight measures are implemented and, where applicable, that records generated by certain AI systems are retained.
Human oversight is especially important. Artificial intelligence can accelerate processes, facilitate analysis and generate high-quality content. What it cannot do is transfer legal responsibility to the technology itself. Responsibility towards customers, regulatory authorities and the courts continues to rest with the business.
Accordingly, every organisation should ask itself a simple question: which decisions are we effectively leaving to artificial intelligence, and which should continue to be subject to meaningful human review?
Answering that question is likely to be the first step towards establishing effective AI governance.
AI and enforcement: fines and legal risks for businesses
The AI Act introduces an enforcement regime inspired by the GDPR. Compliance is no longer simply regarded as best practice; it is a legal obligation supported by a robust system of administrative penalties.
Article 99 of the AI Act establishes different levels of fines depending on the seriousness of the infringement.
The most serious breaches, including those involving prohibited AI practices, may result in administrative fines of up to €35 million or 7% of the undertaking’s total worldwide annual turnover, whichever is higher.
Breaches of other obligations under the Regulation, including certain obligations applicable to providers, importers, distributors and deployers of AI systems, may attract fines of up to €15 million or 3% of the undertaking’s total worldwide annual turnover, whichever is higher.
Finally, providing incorrect, incomplete or misleading information to the competent authorities may result in fines of up to €7.5 million or 1% of the undertaking’s total worldwide annual turnover, whichever is higher.
However, limiting the analysis of the AI Act to its financial penalties would be a mistake.
The consequences of an inappropriate use of AI may also include customer claims, contractual disputes, data protection infringements and reputational damage that may be difficult to remedy.
In addition, it is becoming increasingly common for large organisations to request information regarding the AI governance practices of their suppliers. It is also foreseeable that, over the coming years, AI governance will become a standard element of legal due diligence in investment transactions and mergers and acquisitions, much as data protection compliance, cybersecurity and corporate compliance already are today.
AI governance as a new competitive advantage
Over the coming years, businesses are likely to experience a transformation comparable to that brought about by the GDPR.
Clients will increasingly ask how organisations use artificial intelligence. Suppliers will require stronger assurances regarding the handling of information. Large companies will introduce specific AI governance provisions into their procurement processes, and public authorities are expected to do the same in the context of public procurement.
Organisations that begin preparing now will not only reduce their legal exposure but also strengthen their competitive position. They will be better equipped to satisfy the expectations of customers and investors, to participate in future corporate transactions and to transform compliance with the AI Act into a genuine business asset.
Conversely, the absence of appropriate governance measures may not only increase regulatory risk. It may also affect the value of the business, lead potential purchasers to seek additional warranties and complicate corporate transactions where artificial intelligence forms part of the company’s ordinary course of business.
In an increasingly digital economy, regulatory compliance is no longer simply about avoiding legal risks. Above all, it is about creating value.
FAQs on AI in business and the AI Act
What is the AI Act and why does it affect the use of AI by businesses?
The AI Act is the European Union’s Regulation on Artificial Intelligence. It establishes a legal framework governing the development, placing on the market and use of AI systems within the European Union. It affects businesses because it imposes obligations relating to safety, transparency, human oversight and risk management when artificial intelligence is used.
Does the AI Act also apply to SMEs?
Yes. The AI Act is not limited to large technology companies. SMEs that use AI tools to prepare reports, automate tasks, generate marketing content, implement chatbots or support internal business processes may also be subject to specific obligations, even where they have not developed their own AI systems.
What obligations should businesses using AI be aware of?
Businesses should identify which AI tools they use, the purposes for which they are used, the information shared with those systems, the identity of the service provider, where the data is stored and whether the provider may reuse that information. They should also implement internal AI policies, provide staff training, review contracts with technology providers and establish appropriate human oversight mechanisms.
What is meant by AI literacy?
AI literacy refers to ensuring that individuals using AI systems on behalf of an organisation understand how those systems operate, appreciate their limitations, recognise the associated risks and know how to use them in accordance with the organisation’s internal policies and the applicable legal framework.
Is employee training on AI mandatory?
Yes. Article 4 of the AI Act requires organisations to take measures to ensure a sufficient level of AI literacy among those using AI systems on their behalf. Consequently, AI training has become an important legal obligation and forms part of an organisation’s broader duty of care.
What transparency obligations does the AI Act impose?
The AI Act requires individuals to be informed when they are interacting with an AI system or when particular content has been generated or manipulated by artificial intelligence. Businesses should therefore assess how AI is used within the organisation and implement appropriate transparency measures wherever required.
Can a business upload confidential information to AI platforms?
Not without first carrying out an appropriate assessment. Uploading contracts, customer information, internal documentation or other confidential material to AI platforms may create risks relating to data protection, trade secrets, intellectual property and contractual liability. Organisations should understand the provider’s terms and conditions and how any uploaded information will be processed before using such tools.
Need legal advice? Visit our practice areas related to the use of artificial intelligence in business:
